Other·Shipped
Codinagent (Jarvis)
A personal task-automation agent with a safety policy, running 24/7
3 providers
5 gears · 3 autonomy modes
- Role
- Solo developer, end to end
- Team
- Solo
- When
- Oct 2026
Problem
Heavy projects were stacking up, and boilerplate plus copy-pasting code took a lot of my time. I first wanted to build my own LLM-based coding agent, but my hardware couldn't support it, so I shifted to features it could handle, like a parser and automations such as pasting code from the clipboard straight into files. That grew into a personal task-automation agent with a web UI, task queue, schedules and Telegram remote control, running 24/7 on my laptop as a background service. It made finishing my other projects easier and faster.
Approach
Flask backend with SSE streaming and a React/Vite UI. A tool-using agent loop rotates across Groq, Gemini and OpenRouter models, with 5 selectable gears (presets). A safety policy classifies every tool call as LOW, MEDIUM, HIGH or DENY under SAFE, ASSISTED or AUTONOMOUS modes, with approval cards. A SQLite queue and scheduler handle tasks.
Result
v1 complete (finished around 11 Oct 2026).
How it fits together
- Web UI or TelegramTelegram limited to my chat ID
- Flask backendSSE streaming, SQLite queue + scheduler
- Agent looprotates Groq / Gemini / OpenRouter
- Safety policyLOW / MEDIUM / HIGH / DENY
- Tool call
Safety ladder
| Tool-call risk | SAFE | ASSISTED | AUTONOMOUS |
|---|---|---|---|
LOW reads, normal source edits, allow-listed commands, web search | Reads run, rest ask | Runs | Runs |
MEDIUM deleting files, editing config, git add/commit, draft emails, schedules | Asks first | Asks first | Runs |
HIGH unlisted shell commands, shell operators, fetching a URL | Asks first | Asks first | Asks first |
DENY paths outside the project, secret files, destructive commands, malformed calls | Blocked | Blocked | Blocked |
Every action is rated, and risky ones wait for approval. HIGH asks in every mode, even AUTONOMOUS, and DENY can't be approved from anywhere, including the phone. In SAFE mode only pure reads (reading files, listing folders, searching, read-only commands like git status) run on their own. If nobody answers an approval, it counts as no. The shell-command rating is heuristic, so this is a safety net, not a guarantee.
Features
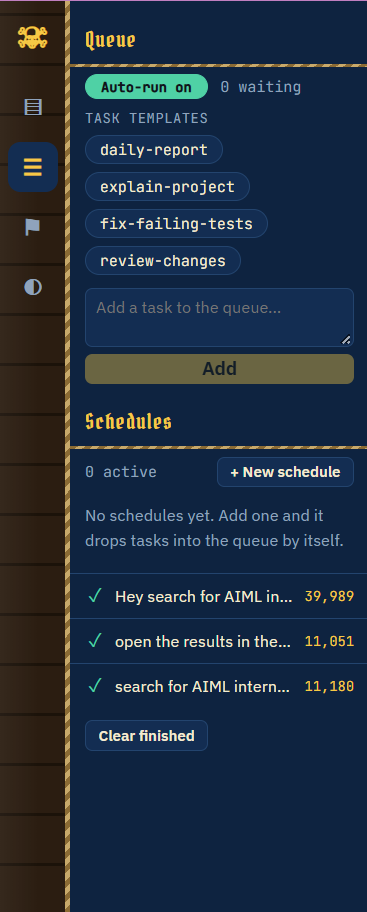
- Web UI with a task queue and schedules
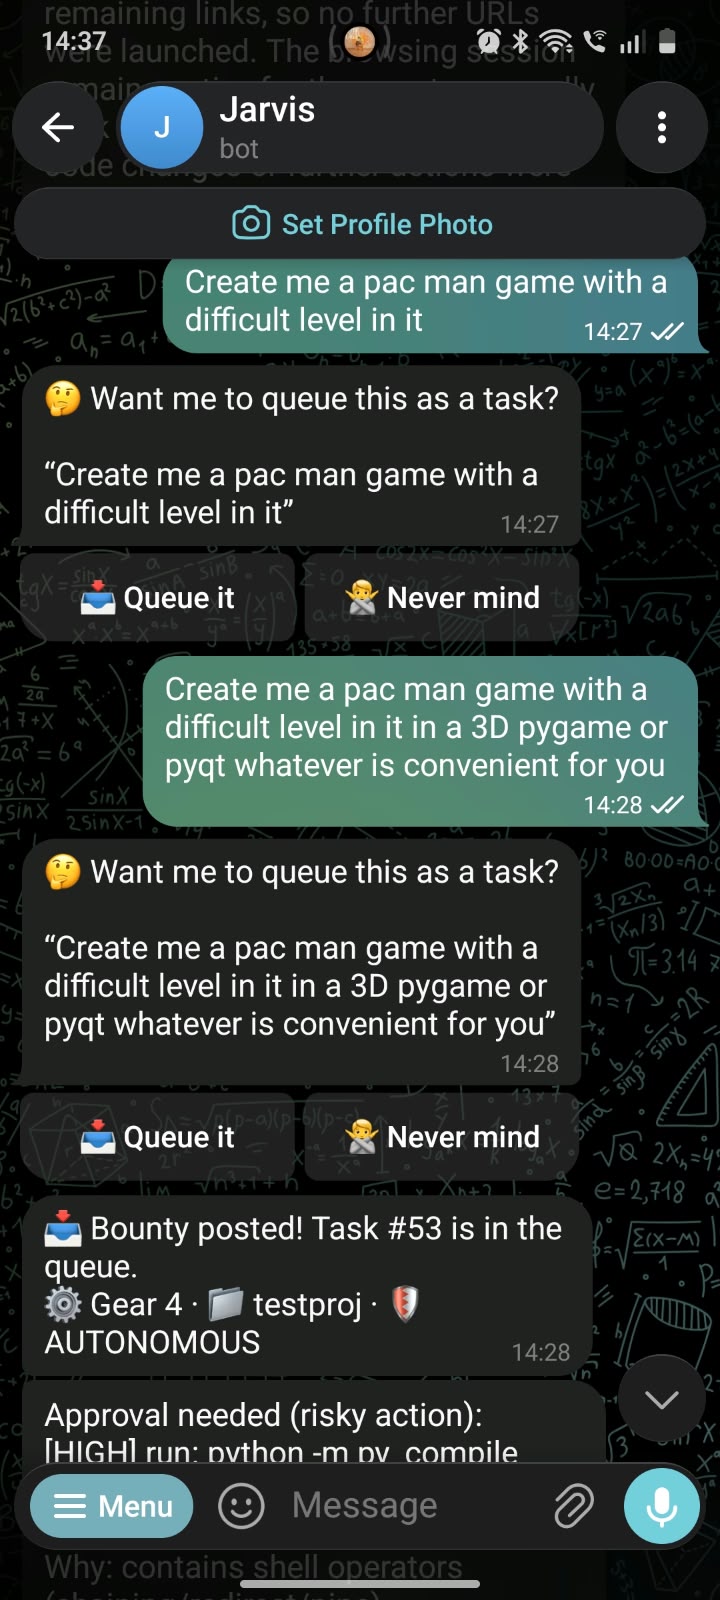
- Telegram remote control, restricted to my own chat ID
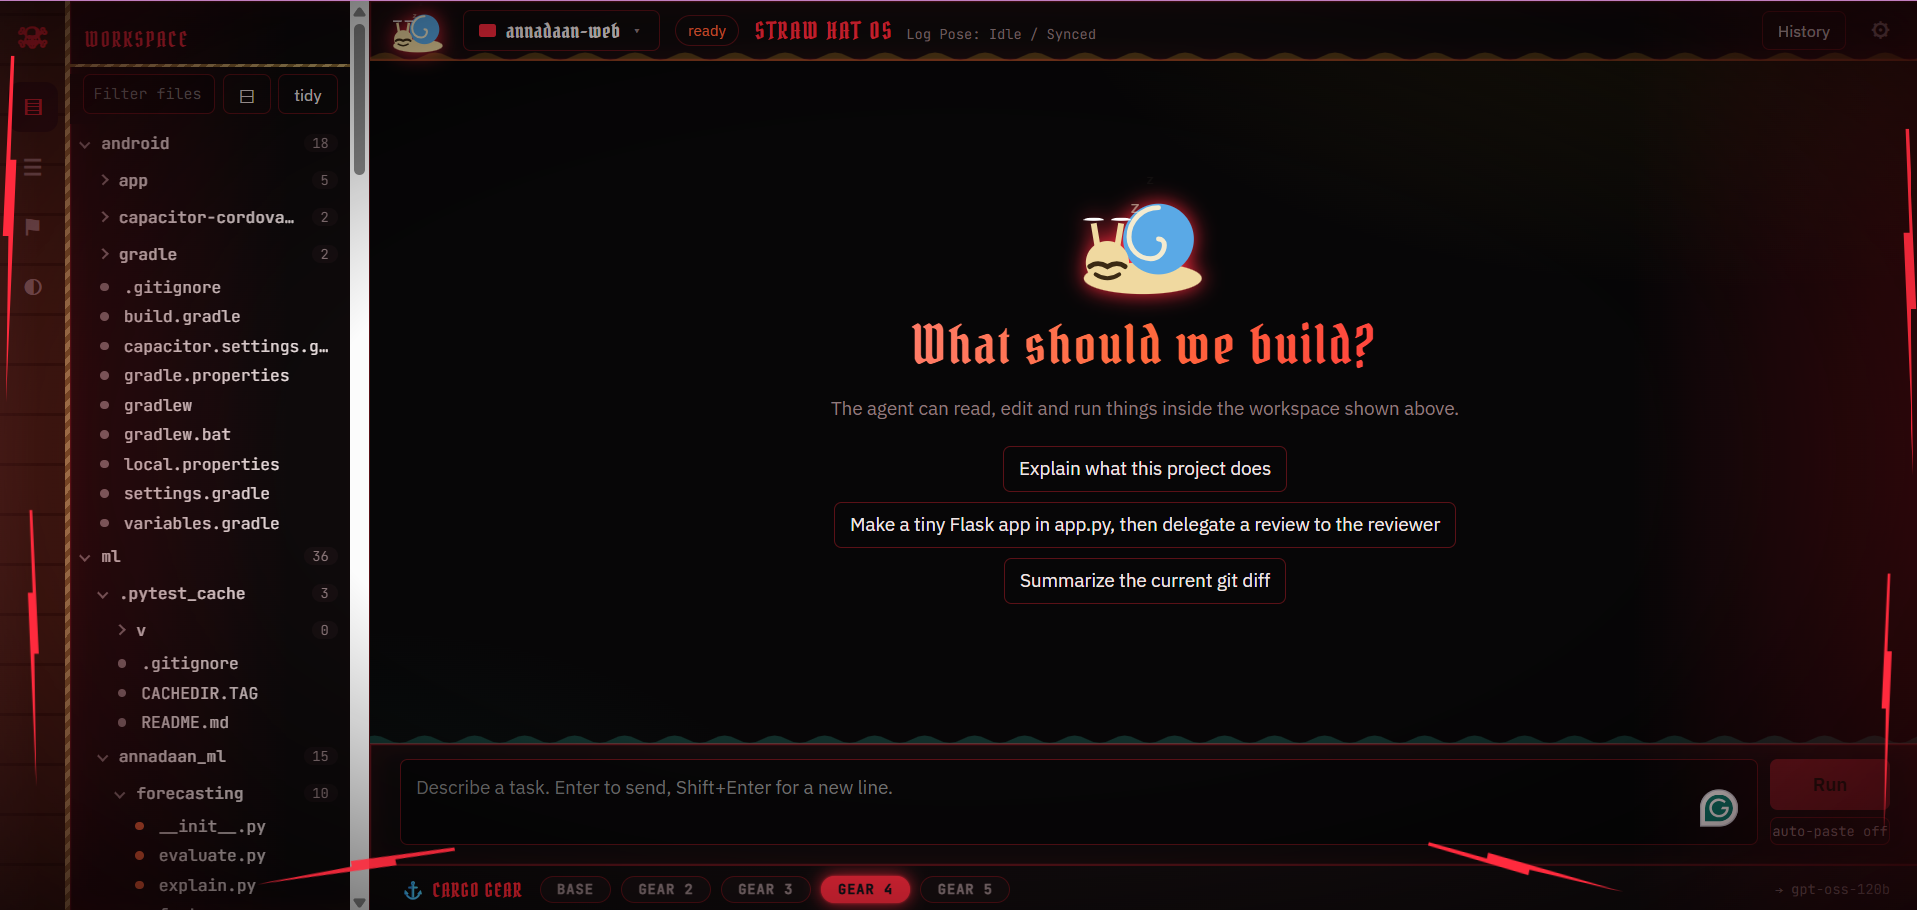
- 5 selectable gears (presets) across 3 model providers
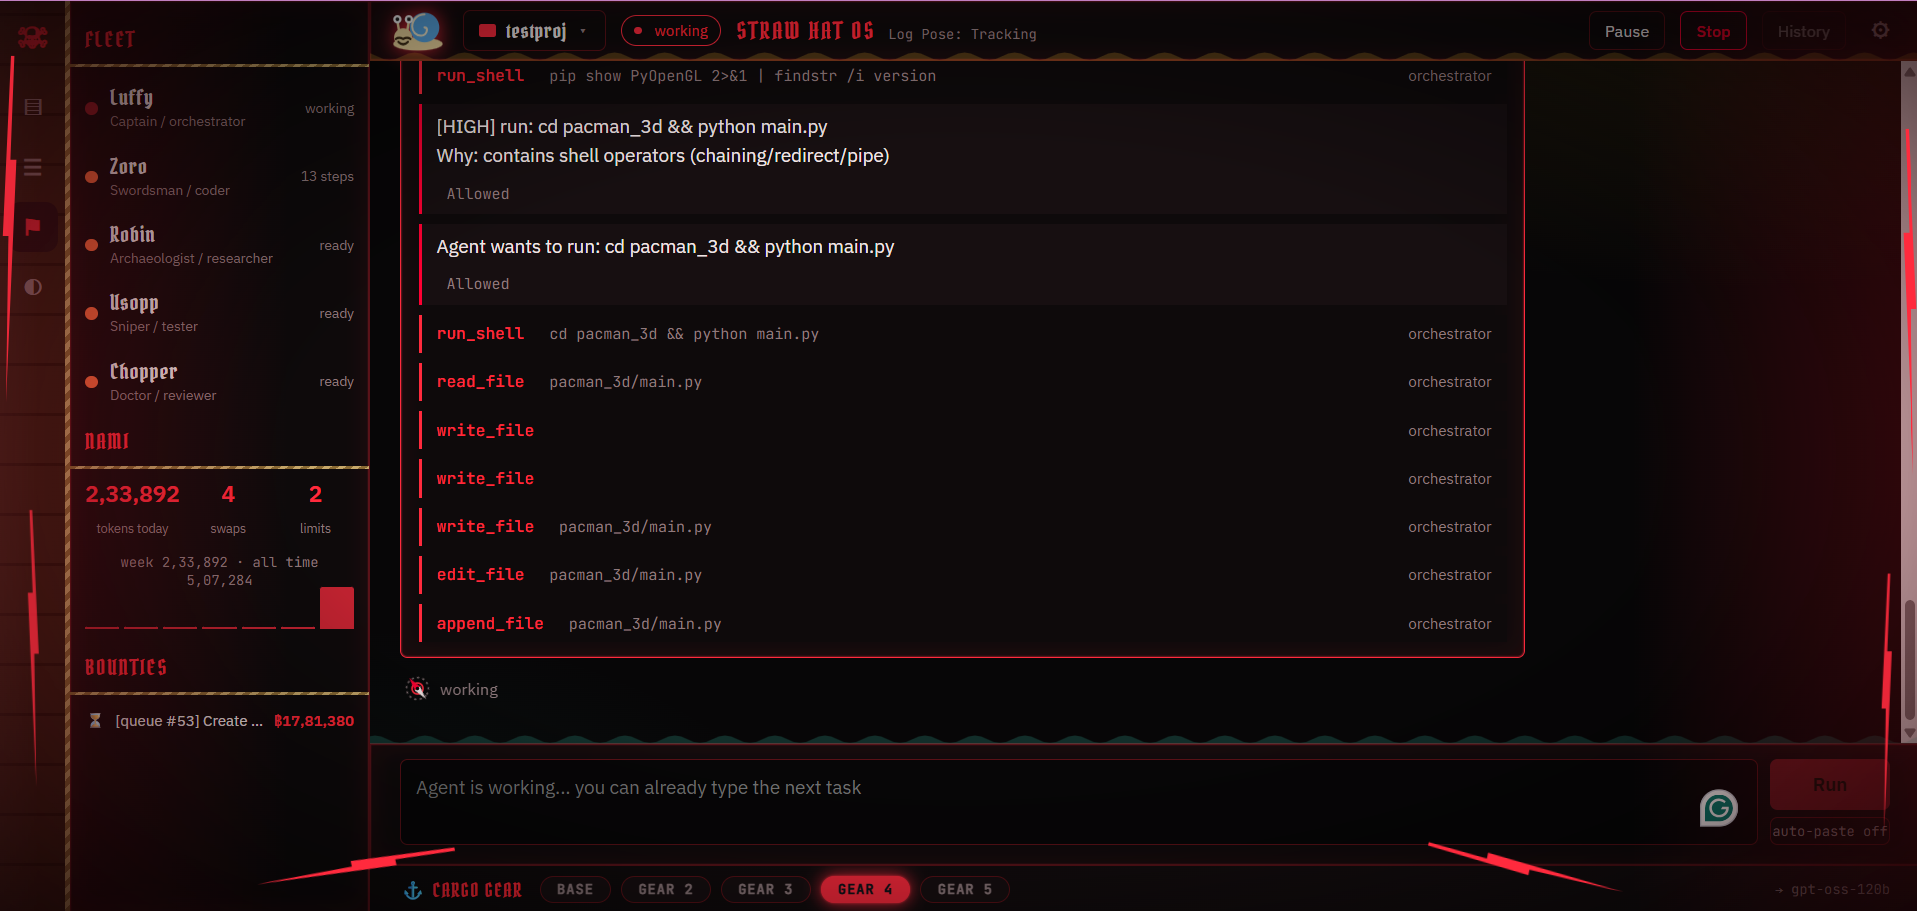
- Approval cards for risky tool calls
- Sub-agent delegation: coder, researcher, tester, reviewer
- /paste applies code blocks to files with no model call
- Secrets redacted from logs
Challenges
Free-tier rate limits, solved by auto-rotating to the next model. The agent also got stuck repeating failing tool calls, so I added a loop guard that nudges it first, then stops and asks.
What I learned
An agent needs guardrails: a safety policy that classifies every tool call, and a loop guard that nudges the agent and then stops to ask when it keeps repeating a failing call. Free-tier rate limits were solved by rotating to the next model automatically. And scoping down to what my hardware could run is what got the project finished.
Tech
PythonFlaskReactViteSQLiteSSEGroqGoogle GeminiOpenRouterTavilyTelegram Bot API
Screens
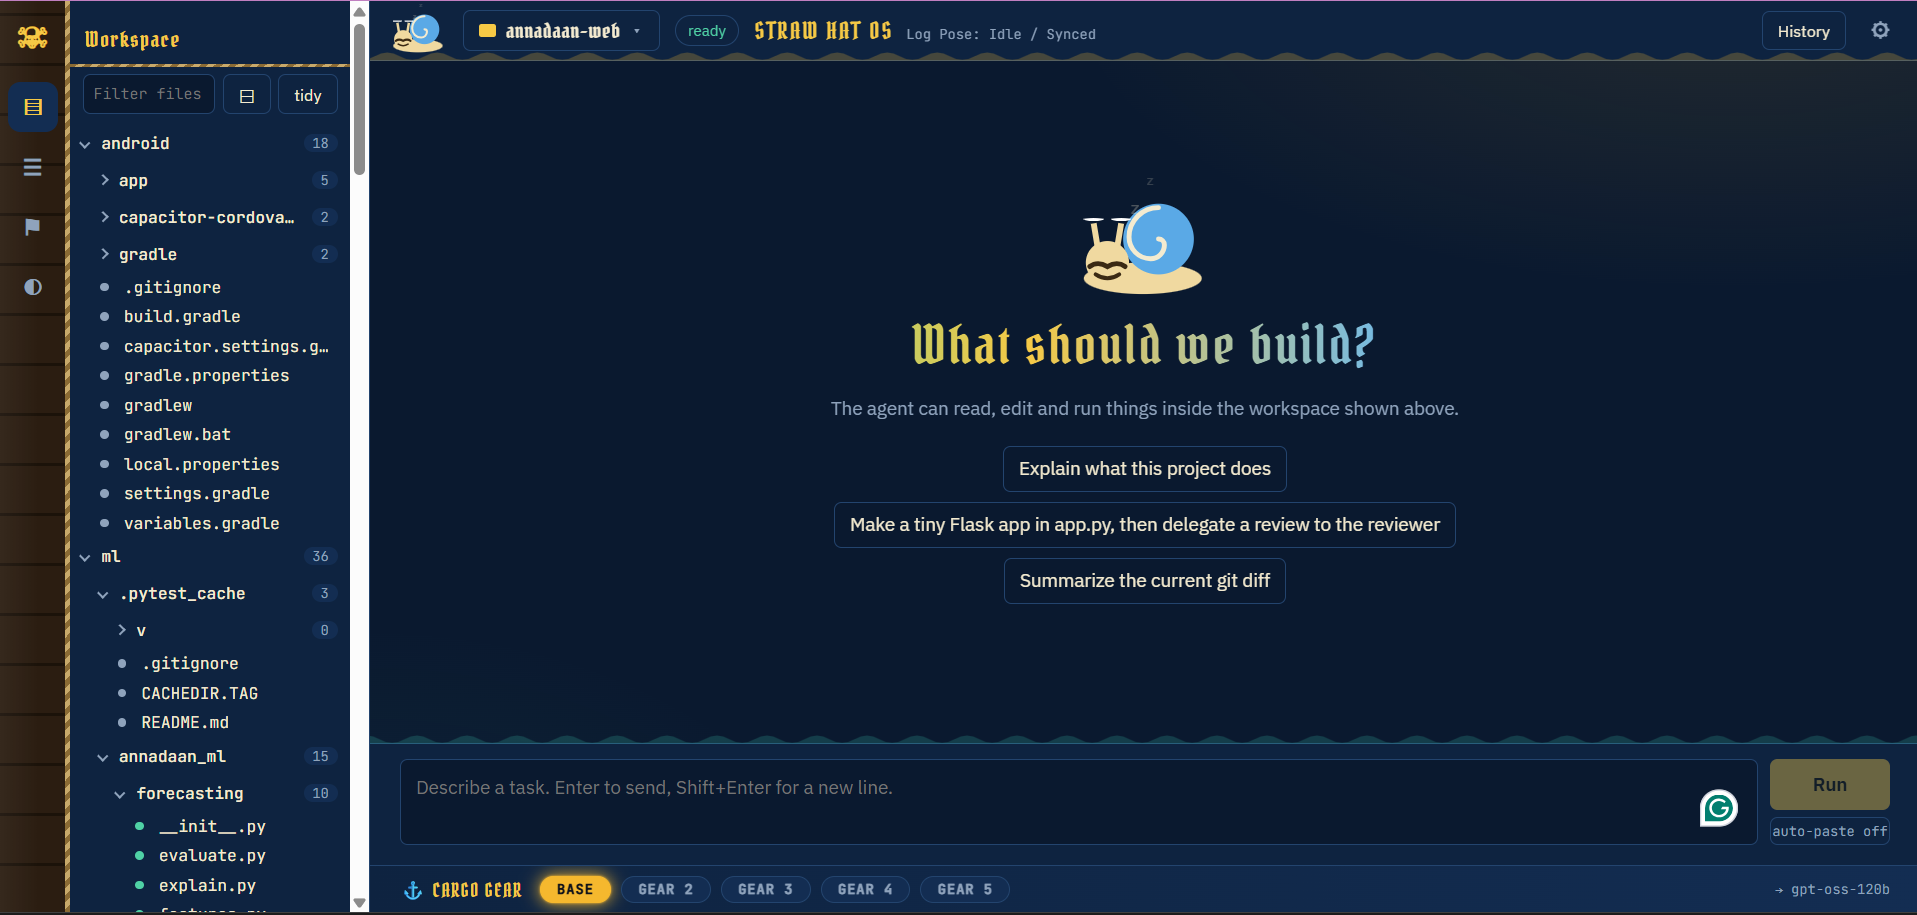
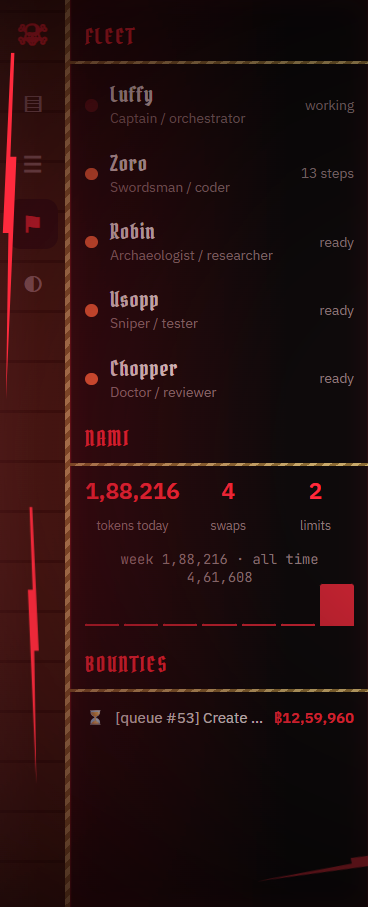
The home page of the agent UI
1 / 6The home page of the agent UI
1 / 6keep scrolling ↓